 Xione Group
Contact Us
Xione Group
Contact Us
Adversaries research their targets long before they strike. Our platform, Metis, is designed to spot these threats and act on them while there is still time.
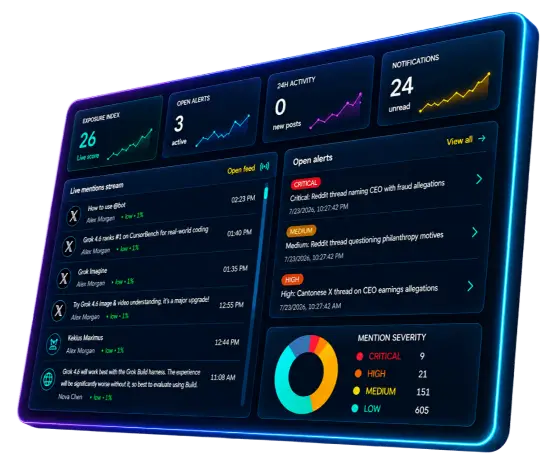
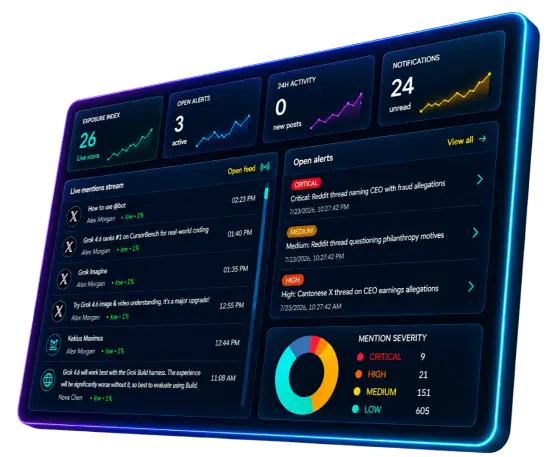
Most organizations only learn about a threat after it has already caused damage. That is where we come in. We stop the threat before it happens.
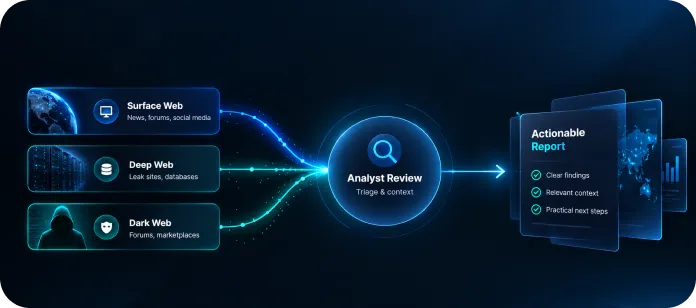
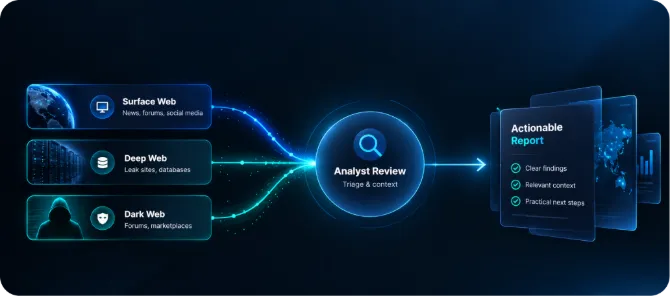
Our analysts combine open-source intelligence (OSINT) tools with technical reconnaissance and continuous dark web monitoring to turn raw signals into actionable insights.
This is not automated alert spam. Every finding, whether it's a case of data exposure, leaked personally identifiable information (PII), or an emerging threat actor is reviewed, contextualized, and prioritized by our analysts.
Engagements can run as a one-time assessment or as ongoing monitoring, giving your organization sustained visibility rather than a single point-in-time snapshot.
We organize our work the way security teams actually use it. From boardroom-level context down to specific, actionable technical findings.
STRATEGIC INTELLIGENCE
High-level context on who is targeting organizations like yours, and why. Built for briefing executives and boards, not just security teams.

Brand & Executive Protection
Detect impersonation, phishing infrastructure, and targeted disinformation aimed at your organization or key personnel.

Threat Actor Attribution
Trace activity back to the individuals, groups, or infrastructure behind a threat, supporting both defensive posture and legal action.
OPERATIONAL INTELLIGENCE
Continuous monitoring of your digital footprint and extended ecosystem, so exposure is caught while it's still just exposure.

OSINT & Dark Web Monitoring
Open-source intelligence (OSINT) combined with continuous surveillance of dark web forums, marketplaces, and leak sites.

Vendor & Third-Party Risk Monitoring
Extend visibility into your supply chain and partner ecosystem to flag exposure that originates outside your own perimeter.
TACTICAL INTELLIGENCE
Concrete technical detail your team can act on immediately whether it is a credential, the domain, or the dataset.

Data Exposure & PII Monitoring
Identify data exposure, compromised credentials, and leaked personally identifiable information (PII) before they're exploited.

Analyst-Reviewed Reports
Regular and ad hoc reporting that translates raw findings into prioritized, actionable guidance.
Built on Investigative Tradecraft
Our threat intelligence team draws on the same forensic and investigative methods we use in digital forensics and corporate investigations.
Human-Reviewed Findings
Every alert that reaches you has been reviewed by an analyst. We prioritize signal over noise, so your team isn't drowning in false positives.
Regional Context
Based in Singapore and Hong Kong, we understand the threat landscape, regulatory environment, and language context across Asia-Pacific in a way global vendors may miss.
From Detection to Emergency Breach Response
When intelligence surfaces something serious such as a confirmed data exposure or PII leak, we can move directly into emergency breach response without bringing in a third party.
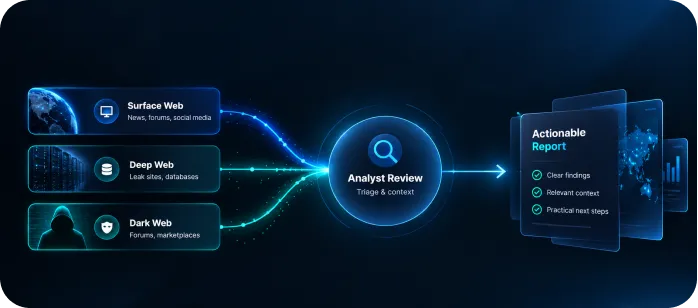
Speak with our team to discover a threat intelligence program tailored to your organization's risk profile, whether it is ongoing monitoring or emergency breach response.